Advertisement
NEAR Intents Halts Services After $3.8M Exploit
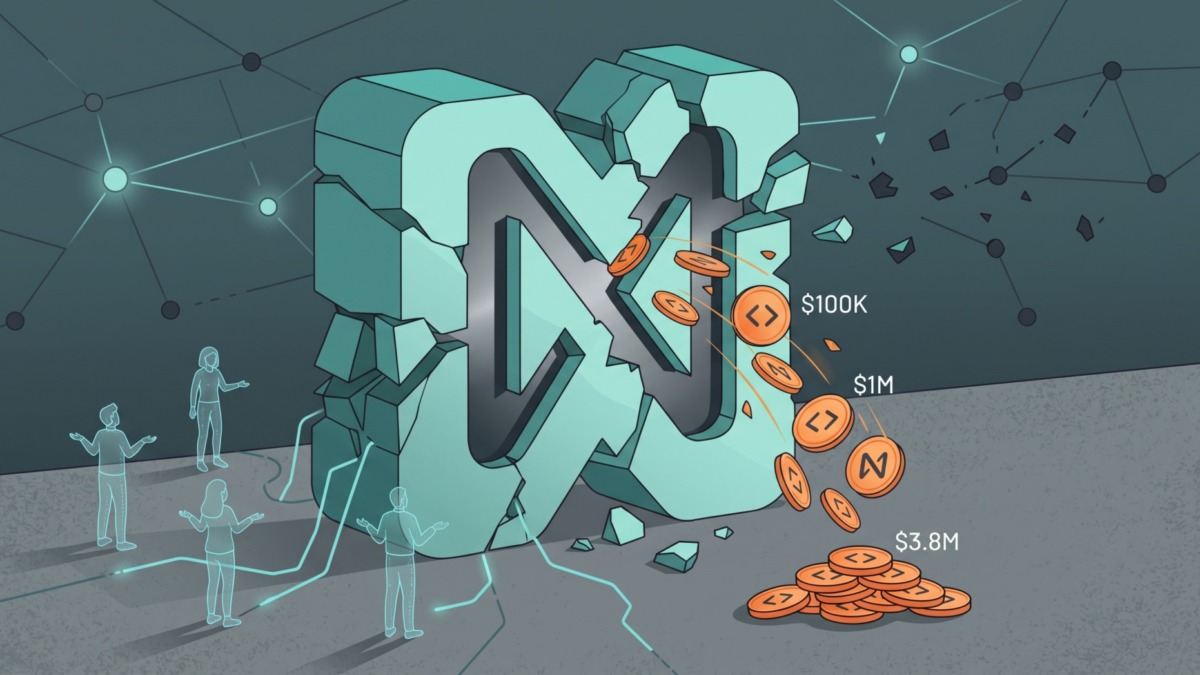
- NEAR Intents lost about US$3.8 million (AU$5.5 million) on Thursday when an attacker exploited a bug between its Omni deposit and withdrawal infrastructure and its smart contract.
- The flaw was patched within an hour, but the platform’s status page still showed open incidents on 11 networks at midday Friday AEST.
- General manager Alex Shevchenko gave the attacker 48 hours to return the funds, days after the platform blocked money linked to the Bitget hack.
NEAR Intents halted its cross-chain trading service on Thursday after an attacker drained about US$3.8 million (AU$5.5 million) through a bug in its Omni deposit and withdrawal infrastructure.
NEAR Intents settles swaps between blockchains through solvers that compete to fill each cross-chain order. In a post on X, the team said the bug lay in the way Omni interacted with the NEAR Intents smart contract. It said the contract-side vulnerability had been patched and that users would be compensated in full.
NEAR co-founder Illia Polosukhin said SHIELD, the AI security layer on Intents, detected the outlier behaviour, and the service was paused. He said the exploit was isolated to USDT on BNB Smart Chain and was fixed within an hour of detection. The core NEAR Protocol, the NEAR token and other applications on NEAR were not affected, he added.
NEAR traded at US$4.90 (AU$7.06) on Friday, down about 5.9% over 24 hours, according to CoinGecko.
Read more: California Bans Public Officials from Launching Memecoins in Rebuke of Trump
Eleven Networks Still Offline
NEAR Intents and its near.com app came back online within hours. Deposits and withdrawals across 11 networks remained suspended while fixes to the Omni infrastructure were completed, with the team saying the pause lasted about 12 hours.
Those networks are BNB Smart Chain, Polygon, TON, Optimism, Avalanche, Stellar, Monad, X Layer, ADI, Scroll and Plasma. Each network still showed an open incident on the NEAR Intents status page at midday Friday AEST.
On-chain investigator ZachXBT reported that the theft began with several irregular outflows from a NEAR Intents hot wallet on BNB Smart Chain. He said the funds went straight to the KuCoin exchange and were bridged into Bitcoin.
NEAR Intents general manager Alex Shevchenko addressed the attacker on X on Friday morning AEST and posted wallet addresses for the money’s return. “We have identified you, sir”, Shevchenko wrote.
He said the window to hand the funds back under responsible disclosure closes after 48 hours. NEAR Intents has also reported the theft to law enforcement and is working with blockchain analytics firms to trace the funds.
Advertisement
The exploit came days after NEAR Intents turned away proceeds of the 24 September Bitget hack. Shevchenko said on 28 September that the hackers had tried to move more than US$50 million (AU$72 million) through the platform. Only US$166,000 (AU$239,000) of the hackers’ funds got through. SHIELD froze another US$503,000 (AU$724,000) mid-transaction.
Polosukhin said NEAR Intents now handles more than US$4 billion (AU$5.8 billion) a month in trading and payments volume. He called Thursday’s breach the first major exploit on the platform.
Bitwise’s spot NEAR ETF, which listed on NYSE Arca on 29 September, names NEAR Intents as the network’s flagship product.
Read more: ESMA Sharpens Crypto Oversight as MiCA Moves From Rules to Supervision

Author
José Oramas
José is a journalist and translator with a keen interest in blockchain and cryptocurrencies.